-
Cybersecurity
- HCL AppScan Scans for application vulnerabilities
- HCL BigFix Secure endpoint management
- HCL BigFix Compliance Ensure security with continuous, real-time compliance monitoring
- HCL BigFix CyberFOCUS Supercharging IT operations to secure the enterprise
- HCL BigFix Remediate Automate, remediate & secure endpoints
- HCL BigFix
- Offerings
-
Products
-
HCL BigFix RemediateFind, prioritize, and fix vulnerabilities across platforms.
-
HCL BigFix LifecycleAutomated device management from provisioning to patching.
-
HCL BigFix ComplianceEnforce continuous compliance with security policies.
-
HCL BigFix InventoryDiscover and manage software and hardware assets.
-
HCL BigFix SaaS ManagementGain visibility and control of SaaS applications to reduce shadow IT.
-
HCL BigFix AEXThe agentic AI platform where autonomy meets governance
-
HCL BigFix Runbook AIAI-driven automation to resolve server and application issues faster.
-
HCL BigFix Cloud Lifecycle ManagementSimplify hybrid and multi-cloud provisioning and resource management.
-
HCL BigFix Service ManagementAI-powered Service Management for IT and beyond
-
HCL BigFix SaaS RemediateClose vulnerabilities faster with cloud-native, automated remediation and patching.
-
- Use Cases
- Industries
- Partners
- Success Stories
-
Resources
-
Get Started with HCL BigFix
-
Help & Support
-
Community
-
Blog
-
HCL BigFix Training
-
Supported Software
-
HCL BigFix Customer Success Stories
-
HCL BigFix Datasheets and White Papers
-
HCL BigFix Days
-
HCL BigFix Trust Center
-
HCL BigFix on LinkedIn
-
HCL BigFix Professional Services
-
Video Gallery
-
All FeaturesThe BigFix product family guide provides an overview of the extensive capabilities...
-
G2
-
offerings-redirect
-
offerings
-
Work From Home
-
BigFix Events & Webinars
-
Past events & webinars
-
Tool Consolidation
-
Simplify Endpoint Management through Tool ConsolidationSignificantly reduce IT costs while also reducing IT complexity, streamlining operations, and esuring business continuity.
-
Download ESG Report
-
BigFix Days
-
Rapid 7
-
InventoryMaintain software audit readiness, mitigate security and non-compliance risks, and better understand software usage.
-
Google Cloud
-
AWS
-
Azure
-
Intel EMA
-
Aruba Clear Pass
-
Service Now Data Flow
-
Service Graph
-
Forescout
-
Resilient
-
Qradar
-
VMWare ESXi
-
BigFix Contact Us
-
BigFix MobileExtends modern endpoint management techniques to mobile devices running iOS, iPadOS and Android -
BigFix ComplianceContinuously monitor and enforce endpoint...
-
BigFix InventoryIdentify licensed and unlicensed software across your organization.
-
BigFix InsightsAccelerate risk identification and decision-making. -
BigFix Trust Center
-
Professional Services
-
BigFix LifecycleReduce cost, risk, and complexity of endpoint and server management.
-
IVR Home
-
ESG-BigFix-IVR
-
Qualys
-
BigFix Field guide
-
Cloud Based Endpoint SecurityEnroll, deploy, secure and support endpoints in today’s work-from-home environment.
-
BigFix Partners
-
Compliance Solution Guide
-
BigFix TrainingA digital workplace with everything employees need.
-
BigFix Days Americas
-
BigFix Days APAC
-
BigFix Days EMEA
-
BigFix Experts
-
Tenable
-
ATMs using BigFix
-
Secure Infrastructure Automation
-
Workspace
-
- Home
- Cybersecurity
- HCL BigFix
- Zero-Day Vulnerability Mitigation Playbook
HCL BigFix
ゼロデイ脆弱性緩和プレイブック:修正パッチ未提供時の次なる一手とは?
Claude MythosやOpenAI DayBreakといった最先端AIモデルは、ベンダーが修正を行うよりも速いスピードで脆弱性を特定し、ゼロデイ脆弱性を発見することでリスク露出のペースを加速させています。そこで鍵となるのは、修正パッチが提供されるまでの間、組織が自社のインフラストラクチャに対してどのようなアプローチを講じるかです。
ゼロデイ脆弱性緩和プレイブックを入手
次のゼロデイ攻撃が発生する前にぜひご一読ください
「目的は、単なる修復や恒久的な問題解決から、ゼロデイ脆弱性を『悪用不可能な状態にする』ことへとシフトします。」
プロダクトマネジメント シニアディレクター
HCLSoftware
「パッチを待つ」アプローチが通用しなくなった理由
問題は欠陥(脆弱性)そのものではなく、その「量」にあります。
セキュリティチームは、出現するすべての脆弱性に直ちにパッチを適用できるわけではありません。毎年何万ものCVEが公開され、AIがさらにそのスピードを加速させる中で、パッチ適用のみに依存する対応キューでは、修正プログラムのテスト、デプロイ、および検証を行う間、リスクが無防備なまま放置されてしまいます。
緩和策(ミティゲーション)の導入が状況を変えます。あらゆるギャップを埋めるために、すべてのパッチが提供されるのを待つ必要はありません。既存のインフラストラクチャを活用することで、今すぐリスクを低減させることができます。
2025年単年で特定された新規CVE数 — 2020年比で263%増加。
情報元: NIST National Vulnerability Database
組織がオープンな脆弱性にパッチを適用するのに要する平均日数
情報元: Verizon DBIR 2026
プレイブックの主な内容 パッチが存在しない状況でゼロデイ攻撃を無効化する10の手法
本プレイブックでは、ベンダーによる修正プログラムを待つことなくゼロデイ攻撃を無力化するために使用される、10のエンドポイント構成戦略を解明します。フレームワークの中核となる3つのコア戦略から着手するのが最も効果的です。
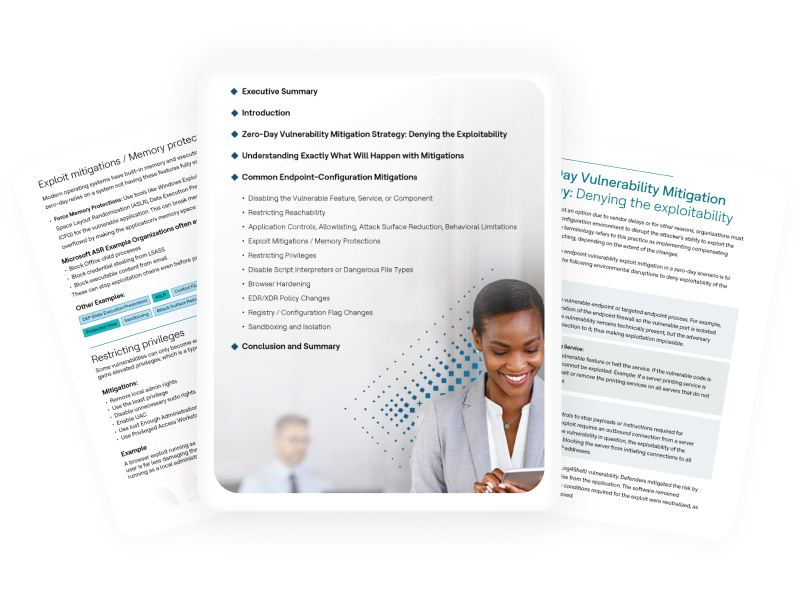
3つのコア戦略
到達性の遮断(Deny Reachability)
脆弱性のあるシステムやプロセスへのアクセスを遮断します。プレイブックで述べる通り、「脆弱性自体は技術的に存在し続けますが、攻撃者が接続を確立できないため、悪用を不可能にします」。
稼働中サービス利用の拒否(Deny Use of the Running Service)
アプリケーション全体ではなく、露出している機能のみを無効化します。原理は明快です:脆弱性のあるコードがメモリ上で実行されていなければ、悪用されることはありません。
ペイロード配送の阻止(Deny the Payload Delivery)
エクスプロイトが実際の攻撃を届けるために必要なネットワーク接続をブロックします。攻撃者が欠陥に到達できたとしても、ペイロードが着弾することはありません。
全環境への迅速な展開と影響の事前把握
組織全体への展開に3週間もかかるようでは、実効性のある緩和策とは言えません。本プレイブックでは、数時間で全環境に対して変更をテスト・デプロイ・監視する方法と、中断する可能性のある機能を事前に把握する手順を解説します。